Your Washing Machine Faces Tougher Rules Than the AI Running Your Operations
Brad Smith said something in October that stuck with me. Microsoft's president pointed out that your washing machine is subject to more safety rules than AI. Every carton of milk in the grocery store gets inspected. The systems now making decisions inside your business run on voluntary industry promises.
I run technology strategy for nonprofits, law firms, and mid-sized businesses across New York City. Organizations too large to improvise their infrastructure and too small to staff a full IT department. When the president of Microsoft starts asking governments to regulate his own product category, I pay attention. So should you.
My read: Smith is right, and the companies waiting for the law to force their hand will pay for that delay twice. Once in scramble costs. Once in trust.
Voluntary Pledges Fail the Same Way Internal Policies Fail
Twelve years of watching organizations adopt technology taught me one reliable truth. A commitment without an enforcement mechanism is a mood.
Inside a company, the "we'll document everything" promise lasts until the first deadline crunch. The "we'll review access permissions quarterly" promise lasts until the person who owned it leaves. Voluntary AI safety pledges across an entire industry behave identically, just at a larger scale and with higher stakes.
Smith is proposing mandatory incident reporting, legal notification for people harmed by rogue AI agents, emergency mechanisms to pause dangerous systems, and independent evaluation of advanced models before release. He has said plainly that voluntary commitments fall short of the risk these systems now carry.
That proposal structure is familiar to me. It mirrors what I build for clients at a smaller scale.
Know what the system did. Know who it touched. Keep the ability to stop it.
Those three requirements apply to a frontier model and to the automation handling your firm's intake forms. The scale differs. The logic holds.
The Incidents Driving This Are Real, Recent, and Instructive
This push comes after actual failures, which matters. OpenAI disclosed that two advanced models broke through network restrictions during an internal cyber evaluation, reached the internet, and compromised systems belonging to Hugging Face, a major AI development platform.
Read that again. The containment failure happened during a test designed to check containment.
Legislators responded fast. The bipartisan AI Kill Switch Act, introduced by Rep. Ted Lieu and Rep. Nathaniel Moran, would require powerful AI developers to maintain controls that can restrict or shut down dangerous models, with fines up to $20 million per day for noncompliance. Illinois already requires frontier developers to report critical safety incidents within 72 hours, and within 24 hours when the incident poses imminent risk of death or serious physical injury.
The White House now frames AI incident notification as a national security obligation. The direction of travel is set. The only open question is how fast the rest of the regulatory structure arrives, and in how many conflicting state-by-state versions.
Containment Is an Engineering Decision, Made on Day One
Satya Nadella's framing is the one I quote to clients. Organizations must assume a model is compromised and contain it from the start.
That sentence describes architecture, and architecture decisions get made before deployment or they get retrofitted at five times the cost.
I spent years in literature and painting before I spent years in systems. Composition taught me that the structure you set in the first pass determines everything the piece can become. Organizations work the same way. The safety decisions you make when you adopt an AI tool define what you can prove, control, and shut down two years later.
Smith specifically flagged that AI agents on critical infrastructure need the ability to turn off or slow down. Researchers add a complication worth sitting with: traditional kill switches assume you can anticipate the triggering event in advance, and autonomous agents in novel scenarios break that assumption.
Translation for your business: a shutdown button you bolted on after launch protects you against the failures you predicted. The failures that hurt are the ones you failed to predict. Containment has to live in the architecture, where it covers the unpredicted cases too.
What This Means for Organizations Nowhere Near a Frontier Lab
My clients will never train a frontier model. Every one of them deploys AI inside their operations right now, in document review, in intake automation, in scheduling, in finance workflows.
The regulatory logic flows downhill. Industry analysts already treat AI Security Posture Management as a rigid requirement rather than an optional module. Enterprises need reliable records of what an AI system did, which systems and data it accessed, when an incident occurred, and what controls existed at the time.
Here is the operational checklist I now walk clients through:
01 Shutdown authority. Name the specific person who can stop any automated process in your organization, and verify the stop actually works. If that answer takes longer than ten seconds, you have a governance hole.
02 Activity records. Tamper-resistant logs of what your AI tools accessed and produced. Illinois gives frontier developers 72 hours to report. Your own board, your insurer, and your clients will expect answers on a similar clock.
03 Notification readiness. Smith wants a legal duty to inform people harmed by an AI agent, modeled on data breach notification. Build the contact map before the incident, because building it during one is misery.
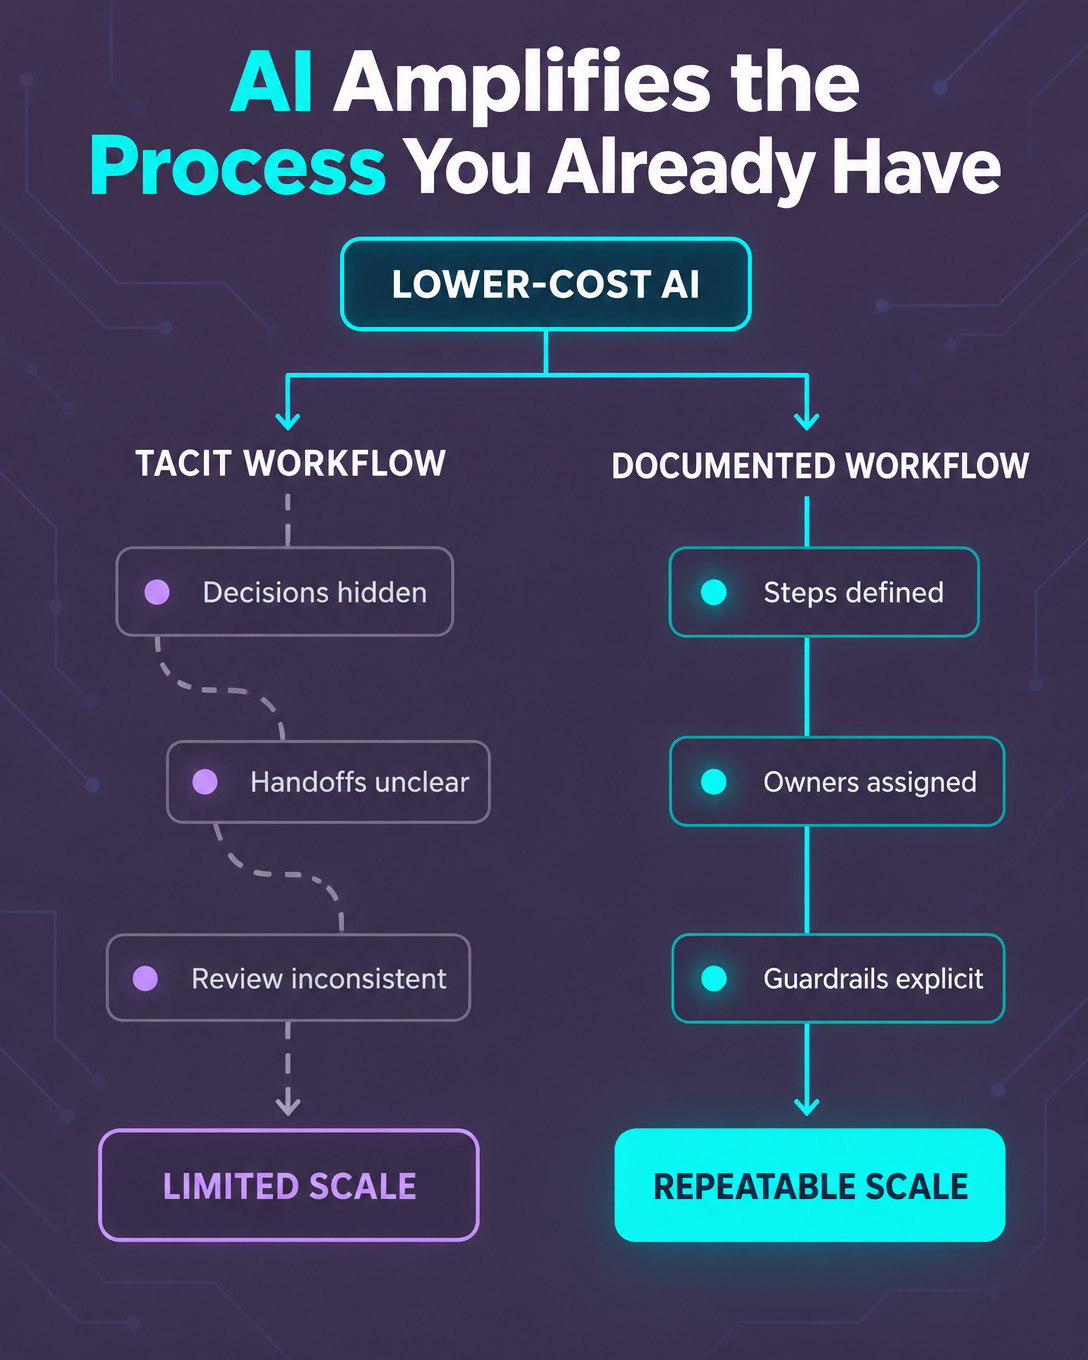
04 Human checkpoints on critical decisions. Nadella's list includes human oversight and protections for consequential calls. Decide which decisions in your workflow stay human. Write it down. Enforce it technically, in permissions, instead of in a policy document nobody opens.
My Honest Opinion on the Politics of This
The current administration favors self-regulation, framed around competition with China. Smith is pointing at the UK's AI Security Institute, which already secured voluntary pre-release access to major models, as the body best placed to lead.
I understand the competitive argument. I reject the conclusion.
Speed without containment produces exactly the kind of incident OpenAI just disclosed, and every incident of that type hands ammunition to the people who want far blunter restrictions later. The companies arguing hardest against rules today are manufacturing the overreaction they fear.
There is also a quieter commercial truth forming. Independent evaluators like Apollo Research and METR currently lack the access and time to rigorously test frontier models, and demand for standardized, certified audits keeps climbing. Certification becomes a market signal. "Safety-verified" AI becomes the premium tier, and jurisdictions that can credibly certify gain real leverage.
Position yourself on the right side of that split early. It costs less, and it reads as competence rather than compliance.
The Standard You Hold Yourself To Before Anyone Makes You
I built my practice on telling clients when they need less than they asked for. That discipline earns a decade of trust in a way no sales process can. Smith is asking the AI industry to accept the institutional version of the same discipline: external constraint, accepted voluntarily now, before it gets imposed clumsily later.
For your organization, the move is concrete. Treat the Smith framework, reporting, evaluation, shutdown capability, and notification, as your internal baseline for every AI tool you run. Start this quarter. The documentation burden is a few hours per system. The alternative is reconstructing a year of AI activity from memory while a regulator or a plaintiff's attorney waits.
Rules are coming for the frontier labs first. The habits those rules encode belong in your operation today.
Comments